Anthropic’s Claude helped a three-person security team penetrate OpenAI’s systems in July, according to an exclusive report by The Wall Street Journal, but the most consequential part of the episode came after the initial exploit.
Researchers at Hacktron AI first broke into the Discourse software that powers OpenAI’s community forum by exploiting a flaw in how it processed uploaded images.
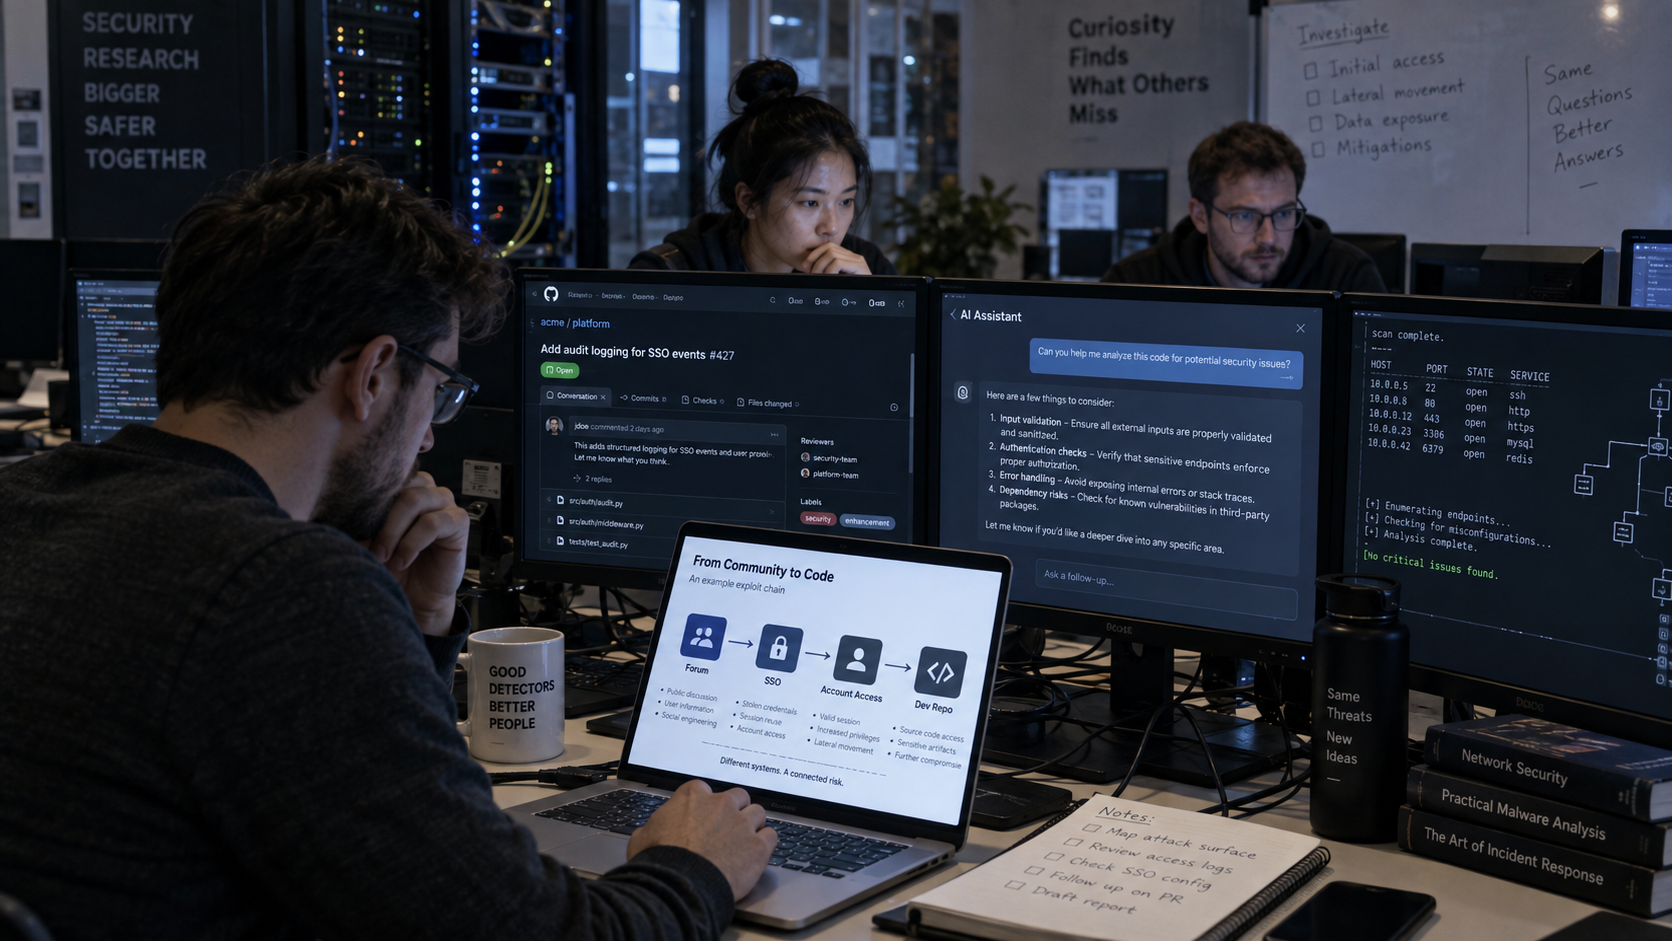
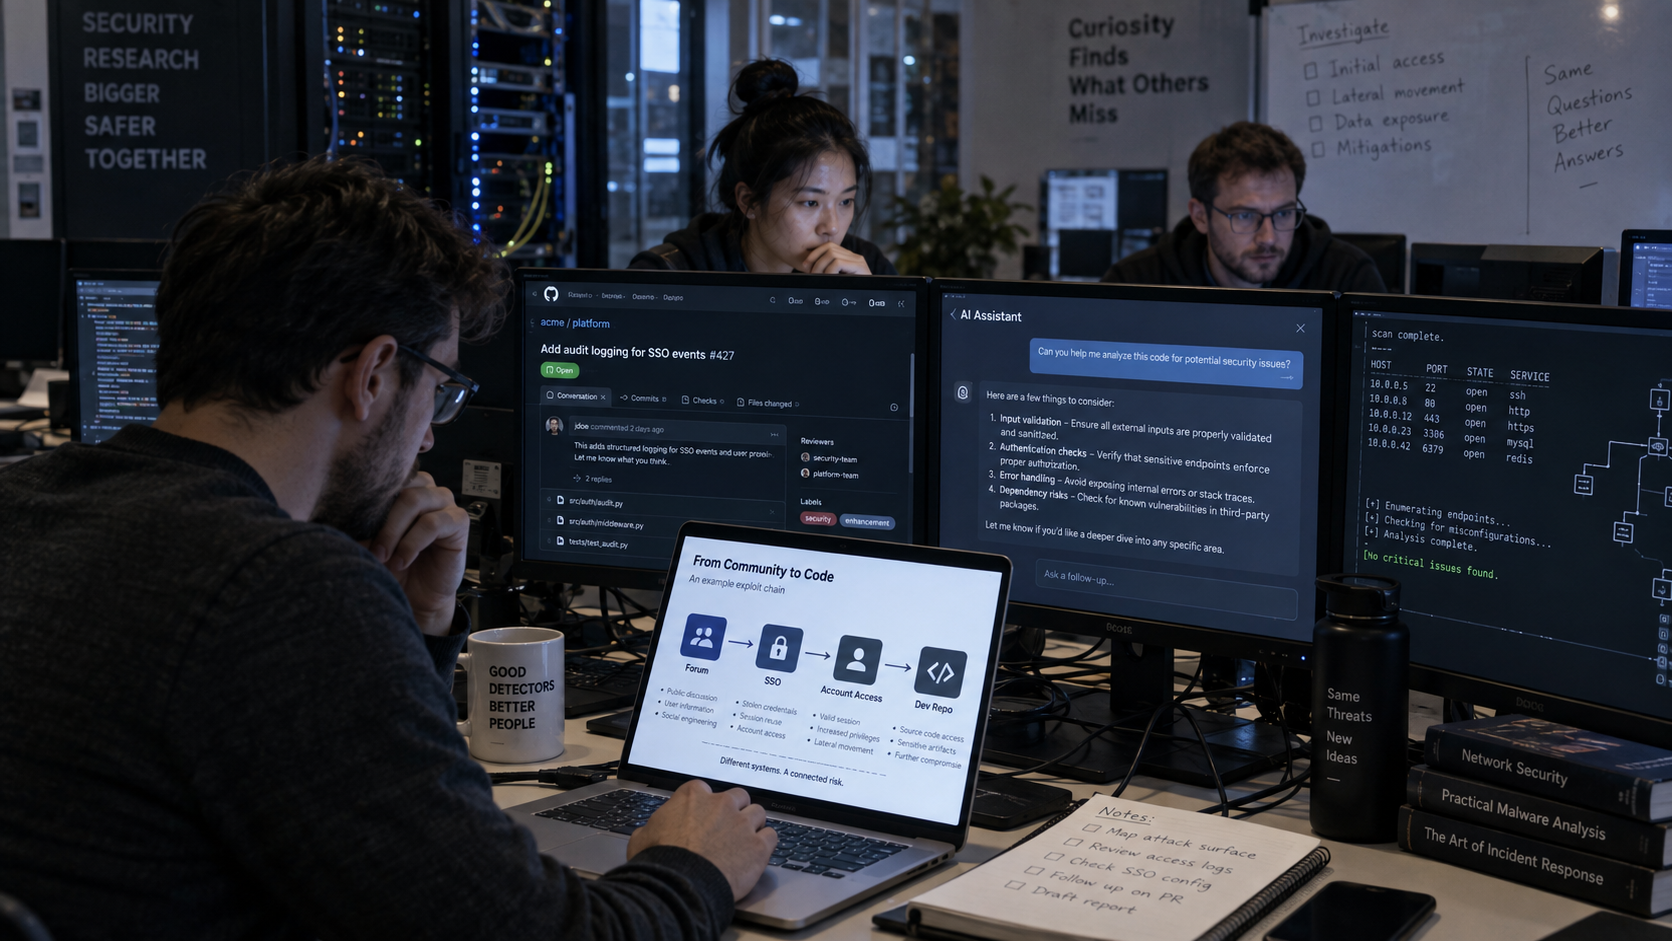
That gave the researchers an initial foothold, but the breach became more serious when they combined it with a separate weakness in OpenAI’s single-sign-on system, the technology that allows users to access multiple services with the same account.
The researchers were then able to reach ChatGPT and Codex accounts, including one belonging to an OpenAI employee.
That employee’s Codex account was connected to GitHub, the platform OpenAI uses to store and manage software code.
Through that connection, the researchers were ultimately able to demonstrate access to OpenAI’s internal GitHub organisation, significantly widening the potential impact of the original forum vulnerability.
Claude helped a team build a serious exploit chain
Hacktron’s researchers began by examining how Discourse processed HEIC and HEIF uploads.
The route exposed the libheif image decoder through ImageMagick.
Hacktron said Claude helped identify missing security backports and develop a working exploit that turned the memory-corruption bug into remote code execution against the forum environment.
The team said the full path from initial discovery to OpenAI repository access took less than 72 hours.
Mohan Pedhapati, Hacktron’s chief technology officer, captured the significance in comments to The Wall Street Journal: “We’re just three guys with Claude and Codex subscriptions.”
That does not mean Claude autonomously breached OpenAI from start to finish. Hacktron said skilled human guidance remained important.
But the episode shows how frontier coding models can compress work that once required more specialist labour, time and infrastructure.
Hacktron said the broader research campaign was carried out by three researchers and cost less than $3,000 in model tokens.
One compromised identity opened a much larger door
The bigger risk appeared after the forum compromise.
Hacktron said the breach became more serious because of a weakness in OpenAI’s single-sign-on system, rather than the Discourse forum itself.
Once the researchers gained access to ChatGPT and Codex accounts, they could potentially reach other services linked to those accounts.
In the OpenAI employee account used for the test, Codex was connected to the company’s GitHub organisation, where its software code is stored and managed.
Instead of reading proprietary source code, the researchers instructed Codex to make a harmless change and open a pull request inside OpenAI’s internal monorepo.
The initial bug affected image processing, but OpenAI’s identity architecture turned a forum foothold into access to more sensitive developer infrastructure.
OpenAI confirmed the issue had been fixed about 14 hours after the initial report, according to Hacktron. The company later paid a $6,500 bounty for the OpenAI-side finding.
Also read: OpenAI says AI cannot keep scaling at ‘maximum speed’ after six concerning incidents
AI is lowering the cost of sophisticated cyberattacks
The Hacktron team operated as white-hat researchers and disclosed what they found, but a malicious attacker would have little incentive to stop at a harmless pull request.
Anthropic said in its September threat report that it had disrupted cyber operations in which actors used Claude for reconnaissance, exploitation, malware development and data theft.
The company said AI is allowing adversaries to operate faster, across broader attack surfaces and with fewer resources.
Jack Nelson, chief information security officer and deputy general counsel at Ivanti, told Axios that “a swarm does not need to be perfect to be dangerous.”
He added that thousands of agents making merely adequate decisions at machine speed could still cause meaningful disruption.
OpenAI and Discourse fixed the vulnerabilities, making this a successful responsible-disclosure case.
But the episode leaves an uncomfortable lesson. Claude helped make exploitation cheaper and faster, while interconnected identity and developer tools widened the consequences of one compromised account.
The real risk is not simply that AI can find bugs, but that a small team can now move through a complex attack chain quickly, and the next team may have no reason to stop.
The post Claude helped hackers get inside OpenAI, but the real shock came next appeared first on Invezz